Profit News Report
No Result
View All Result
  • Investing
  • Stock
  • Economy
  • Editor’s Pick
  • Investing
  • Stock
  • Economy
  • Editor’s Pick
No Result
View All Result
Profit News Report
No Result
View All Result
Home Economy

Hardware Specific Java Glitch Opens Door for Remote Server Takeovers

admin by admin
November 19, 2026
in Economy
0
Hardware Specific Java Glitch Opens Door for Remote Server Takeovers

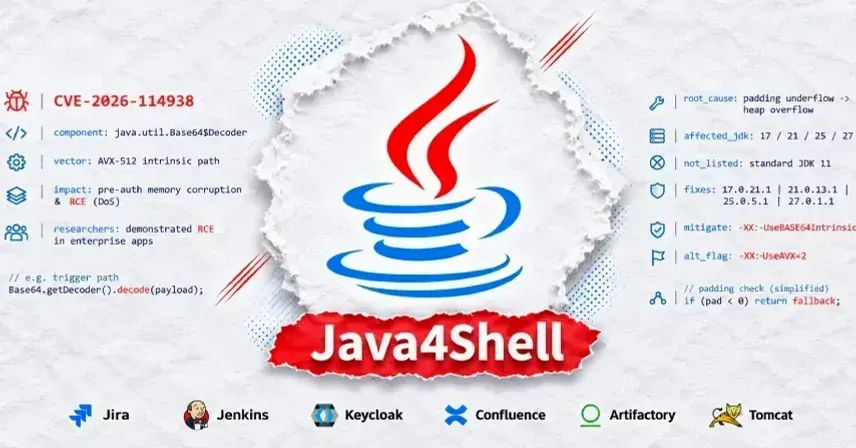
A critical security vulnerability dubbed Java4Shell has sent ripples through the tech community after researchers at the firm Calif revealed that attackers could seize control of high profile servers without needing a password. The flaw, tracked as CVE-2026-114938, allows for pre authentication remote code execution across several industry staples including Jira, Jenkins, and Keycloak. By sending specially crafted strings to services that decode Base64 data, such as login headers or security tokens, hackers can bypass traditional security checks and potentially execute their own commands on a target system.

Interestingly, this vulnerability is not universal but depends heavily on specific hardware configurations. It exclusively affects systems running Java 17.0.6 and later on x86 64 Intel and AMD chips that support a particular performance feature known as AVX 512 VBMI. Because the bug resides in a high speed version of Java’s decoder designed for these specific processors, a single software image might be vulnerable on one server while remaining perfectly safe on another using different architecture, such as ARM64 chips.

To achieve full system compromise, the researchers utilized a sophisticated technique they called JavaBleed. This process involves manipulating the server’s memory to expand neighboring arrays via an overflow, allowing them to read and write sensitive data until they reached the part of Java capable of executing code. While other security labs have successfully triggered system crashes and memory leaks using this method, reproducing full remote code execution has proven more difficult due to dependencies on precise memory layouts and network timing.

In response to the discovery, Oracle and the OpenJDK project have rushed out patches to close the hole. Amazon has already updated its Corretto builds, though Red Hat is still finalizing its fixes. Despite the severity of the flaw, which carries a high CVSS risk score of 9.2 from Calif researchers, Canada’s Cyber Centre reports that there are currently no known instances of this being exploited in active wild attacks. Administrators are urged to check their CPU flags and update their Java installations immediately to mitigate the risk of unauthorized takeovers.

Previous Post

Financial Gains Fail to Quiet the Storm Over Jensen Huang’s Ouster

Next Post

Nvidia Severs Ties With Chinese Market Following Leadership Shakeup

admin

admin

Next Post
Friction in the Skies as Transportation Secretary Faces Fire Over Massive FAA Funding Request

Friction in the Skies as Transportation Secretary Faces Fire Over Massive FAA Funding Request

Recent News

Prediction Market Pioneer Kalshi Sets Sights on Equity Markets

Prediction Market Pioneer Kalshi Sets Sights on Equity Markets

November 18, 2026
Beyond Market Cap: How Rob Arnott Is Hunting For Undervalued Giants

Beyond Market Cap: How Rob Arnott Is Hunting For Undervalued Giants

November 18, 2026
Tech Pivot and Tight Belts Drive Disney’s Latest Financial Win

Tech Pivot and Tight Belts Drive Disney’s Latest Financial Win

November 18, 2026
AI Giant Anthropic Prepares for Historic Wall Street Debut Amid High Stakes and Hype

AI Giant Anthropic Prepares for Historic Wall Street Debut Amid High Stakes and Hype

November 18, 2026

    Sign up for our newsletter to receive the latest insights, updates, and exclusive content straight to your inbox! Whether it's industry news, expert advice, or inspiring stories, we bring you valuable information that you won't find anywhere else. Stay connected with us!


    By opting in you agree to receive emails from us and our affiliates. Your information is secure and your privacy is protected.

    • About us
    • Contact us
    • Privacy Policy
    • Terms & Conditions
    • About us
    • Contact us
    • Privacy Policy
    • Terms & Conditions

    Disclaimer: Profitnewsreport.com, its managers, its employees, and assigns (collectively “The Company”) do not make any guarantee or warranty about what is advertised above. Information provided by this website is for research purposes only and should not be considered as personalized financial advice. The Company is not affiliated with, nor does it receive compensation from, any specific security. The Company is not registered or licensed by any governing body in any jurisdiction to give investing advice or provide investment recommendation. Any investments recommended here should be taken into consideration only after consulting with your investment advisor and after reviewing the prospectus or financial statements of the company.
    Copyright © 2026 Profitnewsreport.com

    No Result
    View All Result
    • About us
    • Contact us
    • Privacy Policy
    • Terms & Conditions
    • Thank you

    Disclaimer: Profitnewsreport.com, its managers, its employees, and assigns (collectively “The Company”) do not make any guarantee or warranty about what is advertised above. Information provided by this website is for research purposes only and should not be considered as personalized financial advice. The Company is not affiliated with, nor does it receive compensation from, any specific security. The Company is not registered or licensed by any governing body in any jurisdiction to give investing advice or provide investment recommendation. Any investments recommended here should be taken into consideration only after consulting with your investment advisor and after reviewing the prospectus or financial statements of the company.
    Copyright © 2026 Profitnewsreport.com